A Python security automation tool that collects system evidence, checks it against NIST SP 800-53 controls, and detects configuration drift between runs.
Date: October 10, 2026Language: Python 3.11.9Platform: Kali LinuxScripts: 2Controls Mapped: 3
2
Scripts Built
3
NIST Controls Mapped
3
Evidence Categories
1
Drift Detected
Environment
Field
Detail
Platform
Kali Linux 2025 (VMware Workstation)
Language
Python 3.11.9
Editor
GNU nano 8.1
Evidence Sources
/etc/passwd, /etc/ssh/sshd_config, /etc/sudoers
Output Format
Timestamped JSON
Scripts
collect.py, check.py
Working Directory
~/lab30
Script 1 — Evidence Collector
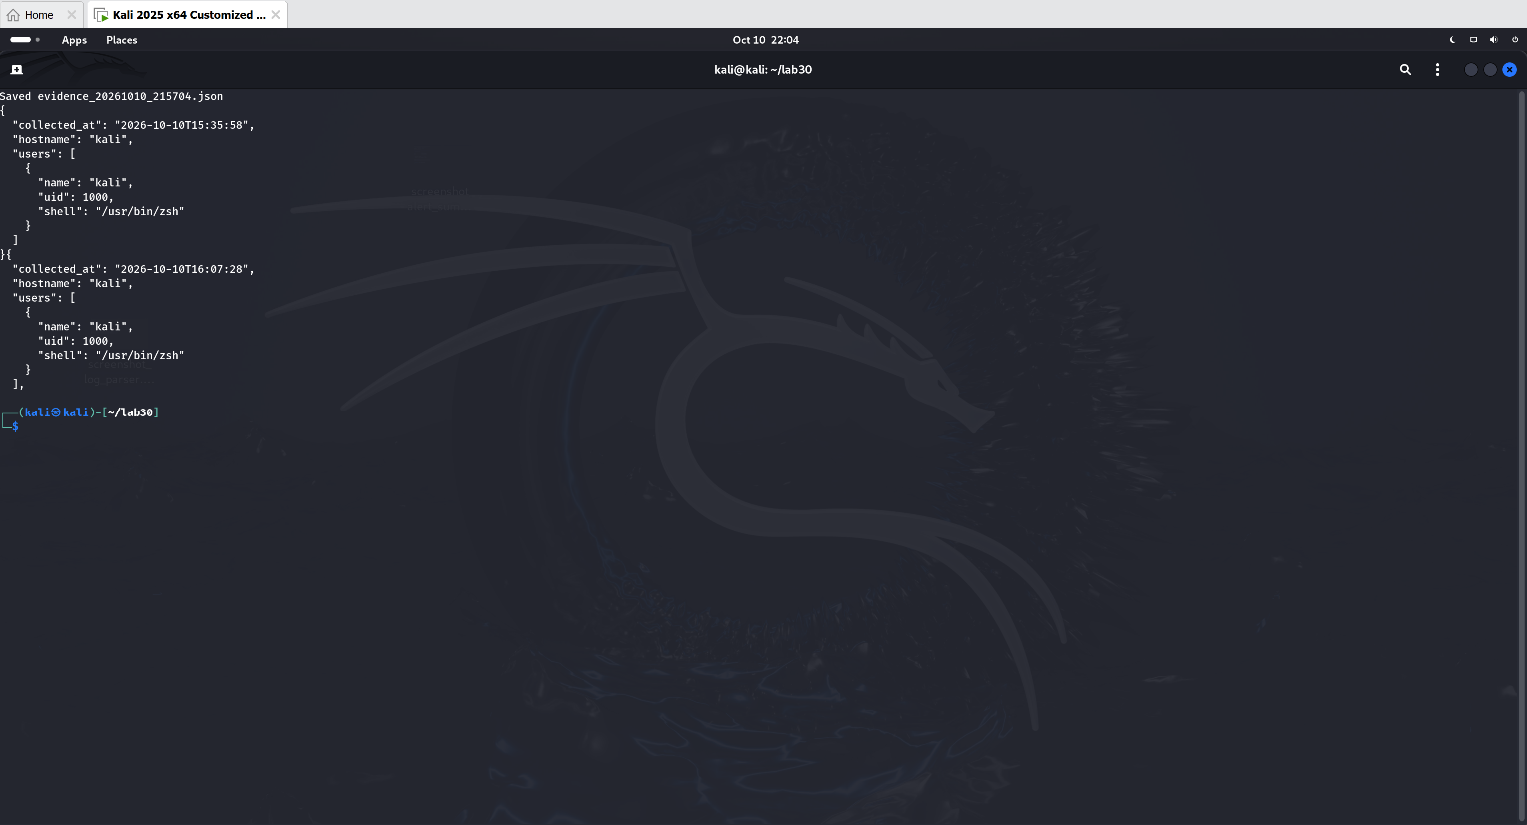
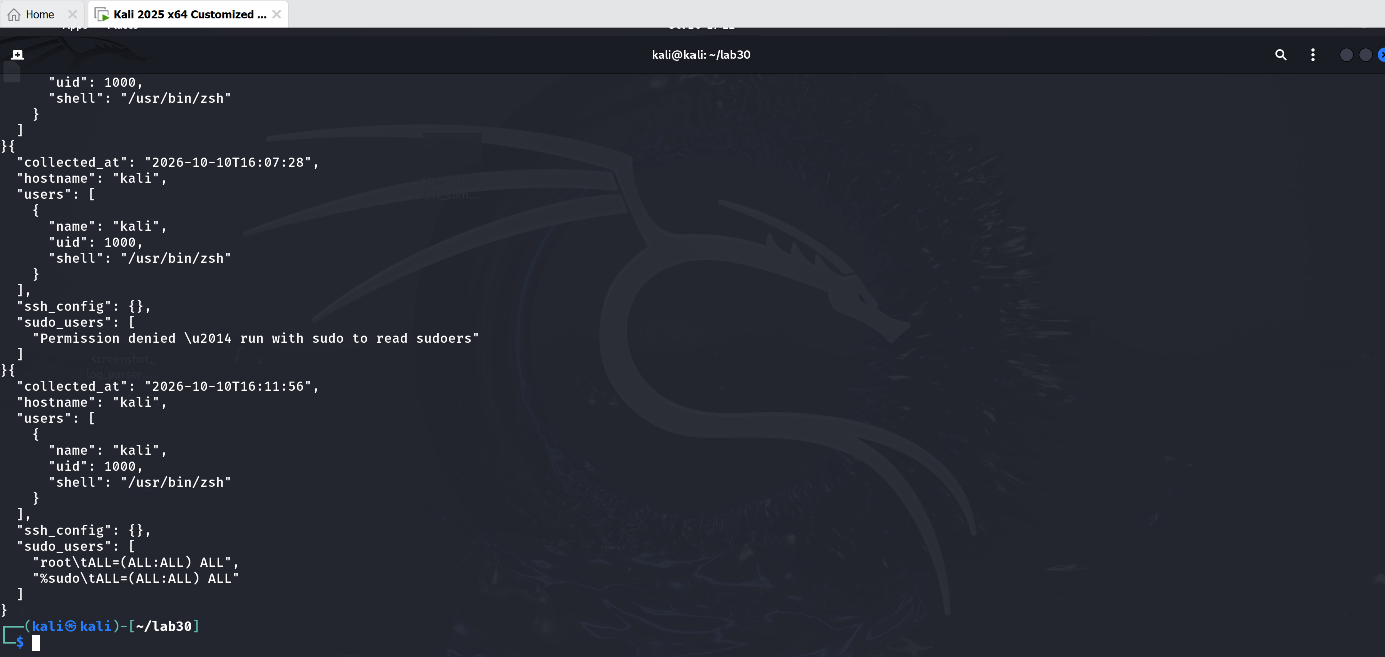
collect.py reads three system sources and saves the findings to a timestamped JSON file. Each run produces a new snapshot that can be compared against previous runs for drift detection.
Evidence collected per run:
Interactive user accounts from /etc/passwd (uid ≥ 1000)
SSH configuration from /etc/ssh/sshd_config
Sudo rights from /etc/sudoers
Step 1 — collect.py — timestamped JSON evidence file saved successfullyStep 2 — collect.py expanded — SSH config and sudo rights now included in evidence
Script 2 — Baseline Checker and Drift Detector
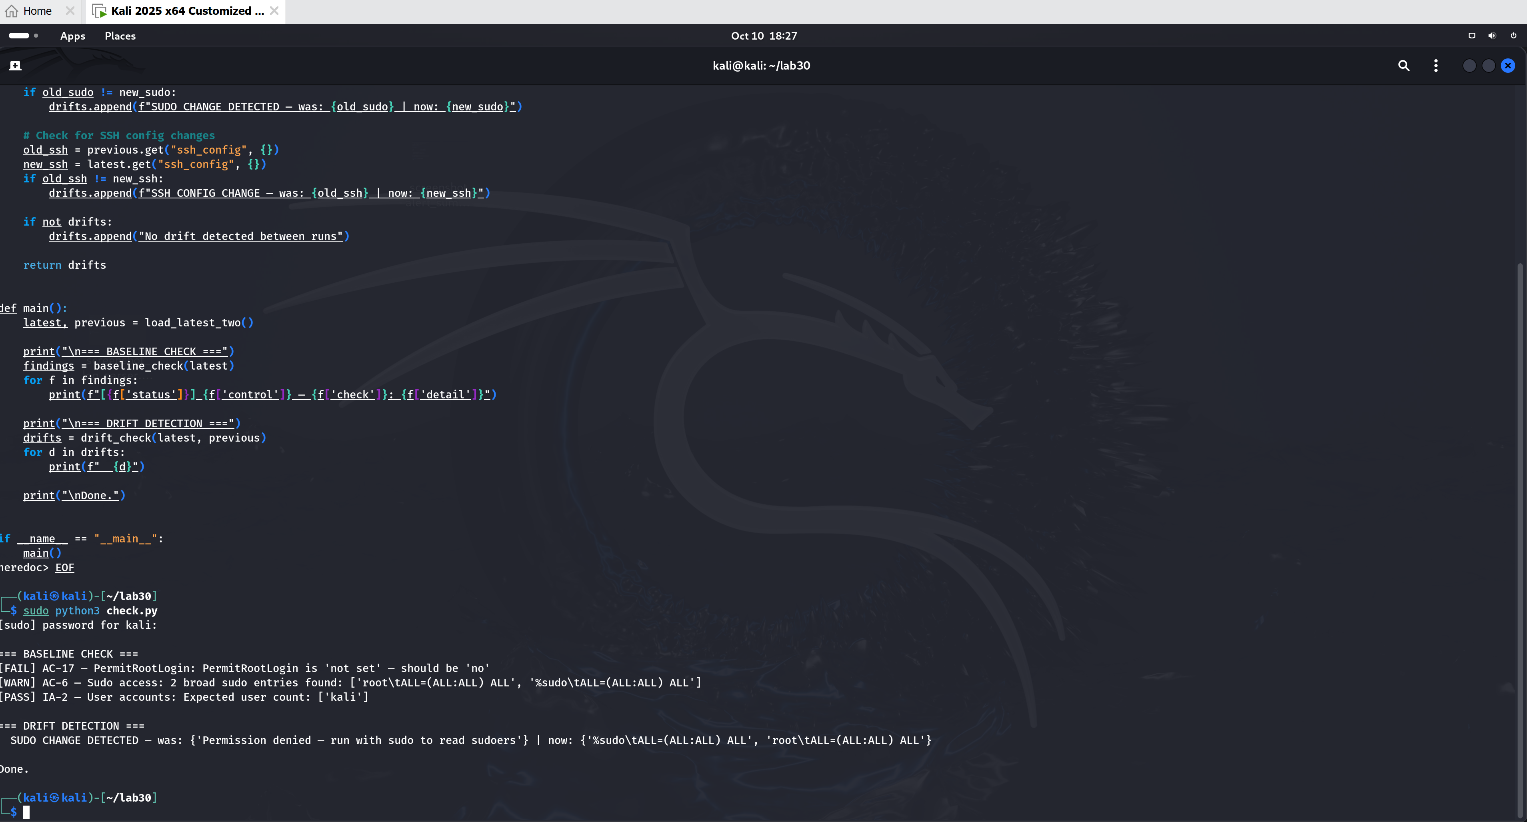
check.py loads the two most recent evidence snapshots. It runs each finding through a set of NIST SP 800-53 rules and flags any change between runs as configuration drift.
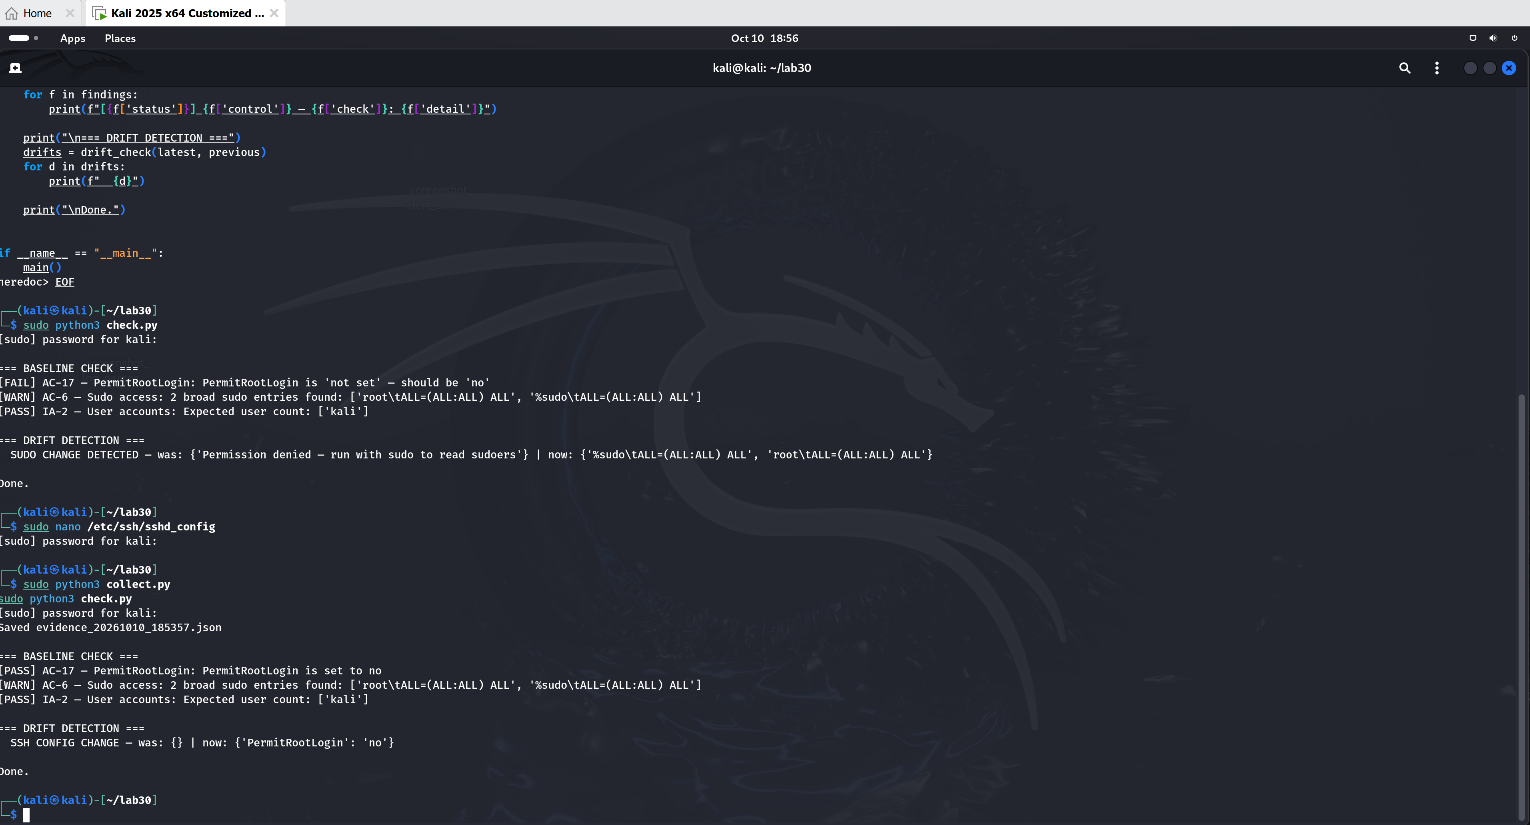
To validate drift detection, PermitRootLogin no was deliberately added to /etc/ssh/sshd_config. A new evidence snapshot was collected and check.py was run against it.
Step 4 — self-test — PermitRootLogin set to no; AC-17 flips from FAIL to PASS; drift detected
Detection Engineering Insights
This lab demonstrates the core loop of any configuration monitoring system: collect a snapshot, compare it to a baseline, flag what changed. The same pattern underlies enterprise tools like AWS Config, Azure Policy, and Qualys Policy Compliance — this tool implements that logic from scratch in Python.
Key engineering decisions made during the build:
Evidence is stored as timestamped JSON so every run is independently auditable
The sudoers file requires elevated privileges to read — the tool handles PermissionError gracefully and flags it rather than crashing
Drift is detected by comparing Python sets, which handles ordering differences between runs cleanly
FAIL vs WARN distinction mirrors real SOC alert severity: FAIL means a specific requirement is unmet; WARN means something exists that warrants human review
Outcome
▸ collect.py — user accounts, SSH config, and sudo rights collected to timestamped JSON ▸ check.py — NIST SP 800-53 baseline check implemented across 3 controls ▸ Drift detection confirmed — SSH config change caught between runs ▸ AC-17 status changed from FAIL to PASS after PermitRootLogin no was set ▸ Lab 30 confirmed — all scripts functional on Kali Linux